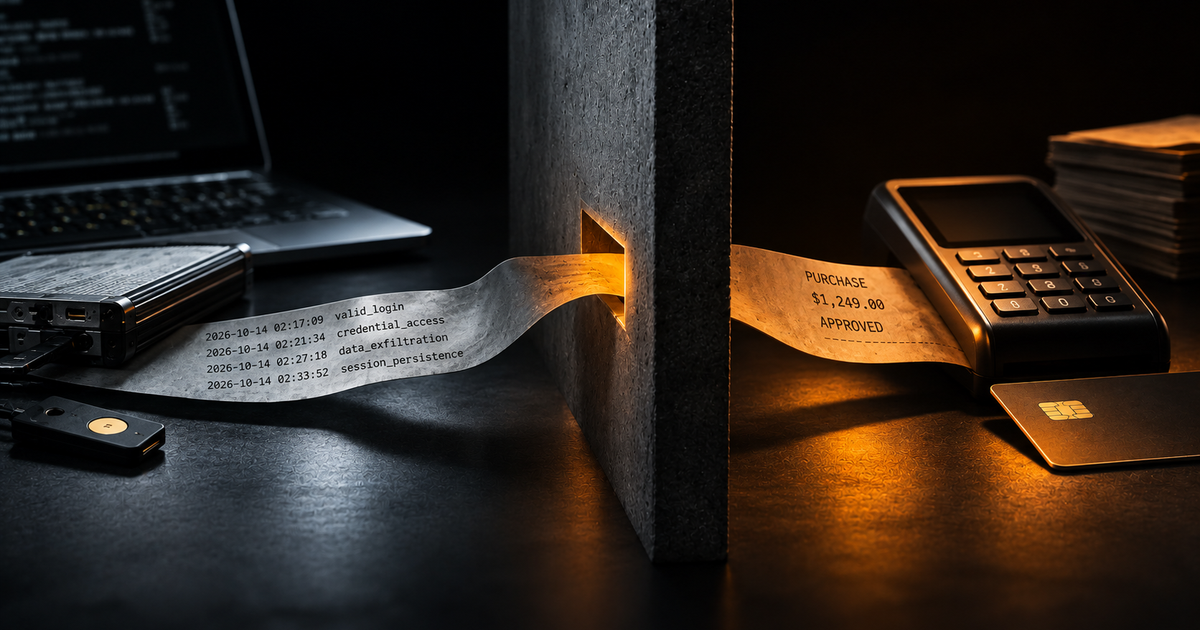

Thesis: The break-in and the fraud are one kill chain. When companies and law enforcement split who investigates what, neither side sees the actor’s whole operation.
Attackers don't organize operations around how their victims divide responsibilities. They organize around objectives. Companies divide investigations by function, which can leave nobody responsible for understanding the entire operation.
One kill chain
Attackers can run one operation.[1] Inside a company, it often becomes at least two separate investigations.
Security teams investigate how actors got in: how they gained access, what they accessed, and what to do afterward. Fraud teams see what the actors did with access to financial data from the operation: purchases, transfers, and payouts.
Each team sees a part of a larger operation. Seeing the entire picture depends on what security and fraud teams share.
Actors are motivated to take action. Often, that motivation is financial. They steal data to sell, hold organizations at ransom, or gain access to other sensitive data. Financial motivations aren’t behind every attack, and not all fraud requires breaking into systems.
Figure 1 · One operation. Partial investigative views.
- Gain system access
Illustrative intrusion-enabled fraud
- Evidence
- Credentials and system access
- Typical starting point
- Security investigation
- Activity before payment
- Evidence
- IP intelligence, referrers and analytics
- Connection needed
- Evidence across security and fraud
- Transactions and payouts
- Evidence
- Purchases, transfers and payouts
- Typical starting point
- Fraud investigation
When intrusion enables fraud, separate investigations see parts of one operation until their evidence is connected.
Putting security practitioners closer to fraud
I managed a team that built a prototype for applying security practitioners’ skills to fraud. They brought experience from incident response, threat intelligence, and threat detection. They knew how to investigate activity across systems, connect evidence, and turn what they learned into detections.
Security practitioner experience expanded what the team could investigate. A transaction might be the clearest evidence of fraud, but the activity leading up to it produces evidence. IP intelligence, referrer headers, and analytics can help explain where traffic came from and what happened before a purchase.
Security practitioners were used to working with those sources.
Action on transactions limits how early you can act. By the time a stolen card is used and a fraud transaction model alerts, attackers have already obtained the card details and reached the purchase stage.
Investigating preceding actor activity gives teams more opportunities to detect the broader operation. This helps us detect fraud earlier and correlate it internally when it happens.
The team also brought hard-learned experience from security and intelligence. For example, they shared vocabulary for actor behavior to make connections easier to establish and communicate.
FT3 is a public example of this approach[2], applying structured data of tactics and techniques to fraud, carrying enough details to other teams or outside of the organization
Why it stays split
Merging fraud and security work changes ownership (investigations, resources, credit for results). Leaders with established teams resist change that could reduce their authority or budget. Practitioners have to worry about new skill-set requirements and responsibilities that will affect their careers.
People are evaluated against their contributions to their organizations. If performance demands get tied to fraud losses or incident-closure metrics, cross-functional investigations take time away from the work output they are evaluated against. Asking teams to collaborate doesn’t resolve this conflict.
This problem also applies to managers. Cross-organizational investigations require them to commit staffing resources to work they may not control, with another team reporting the results.
They have to negotiate who the decision makers are and who is accountable when something is missed.
Successful prototyping doesn’t automatically become a sustainable operating model. Proving that security practitioners can improve fraud investigations is only the start. Making the approach permanent requires leadership to align responsibilities, fund the work, and reward the people contributing to it, both inside and outside the organization.
The sharing gap
Fraud teams often have limited access to traditional intelligence. If they sit apart from the security teams, they can miss both the intelligence that security receives and the community it uses to exchange intelligence.
Fraud intelligence sharing does happen, often centered on payment: stolen cards, disputed transactions, and accounts associated with fraud loss. This data is useful but covers only part of the operation. The infrastructure actors use, their account-creation methods, and how they apply automation can help the broader company detect fraud before the transaction occurs.
Security traditionally has more established tools and practices for that kind of intelligence sharing. Sharing groups give security practitioners relationships they can use during an investigation. Standardized formats, such as STIX/TAXII[3], help teams compare findings programmatically and use them in their detections. The Traffic Light Protocol (TLP) specifies how widely recipients can distribute shared information. These long-standing security practices take work to maintain, but provide practitioners with a way to share information beyond their own organization.
Fraud teams need those capabilities.
That means staff who can develop intelligence from investigations, describe the behavior precisely, and share enough evidence (IOCs) for other teams to act on it. Receiving intelligence also requires someone with the skills to assess it against internal data to turn intelligence into actionable results.
Security teams can help build these disciplines through existing communities, tools, and experience.
Building trust in these relationships takes years.
The immediate work is establishing the cross-organizational relationships now.
Agentic commerce raises the bar
Agentic commerce is here.
AI agents are making purchases and performing financial transactions[4]; fraud investigators will need to deeply understand how those agents operate. A transaction record may show what was bought, from whom, and where the money went.
It won’t necessarily explain why the agent made the purchase, whose instructions it followed, and whether someone manipulated its delegated authority.
Establishing what instructions agents received, which tools they called, what permissions they held, and what they did all require deep technical knowledge of the protocols and software used.
Transaction models still help identify suspicious payments, but determining how an agent was used to commit fraud requires investigations beyond the payment. Security practitioners already work with compromised credentials, prompt injection, permissions abuse, and activity across connected systems.
Fraud teams bring knowledge of financial behavior.
Both are needed to explain what happened.
Companies will have to collect this evidence before they need it. If an agent can perform transactions, but its actions cannot be reconstructed, investigations will fail to distinguish an authorized purchase from an error or deliberate abuse. Fraud and security teams should define these logging requirements as they build agentic commerce systems.
Law enforcement has the same split
Law enforcement faces similar problems when cybercrime and financial crime sit in separate units. Investigations into stolen credentials may be assigned to cybercrime, while the fraud committed with those credentials goes to financial crime. Unless those investigators work together, each misses evidence that connects the access to the transactions and the people behind them.
That doesn’t require merging units. Task forces can bring investigators together around an actor or operation, with shared access to evidence and clear responsibility for following leads. This requires committed staff and agreed priorities.
Referring a case to another unit and waiting for an answer is not good enough.
Close
Companies and law enforcement agencies need to reconsider how they assign and run these investigations at an organizational level.
When an intrusion enables fraud, someone needs the authority to follow the case from initial access through monetization and bring in the right people.
The structure can vary.
What matters is access to data across teams, authority to pursue leads across department boundaries, and a reporting chain that supports the full investigation.